Secure Cloud Solutions: A Plain-English Guide for UK Businesses (2026)

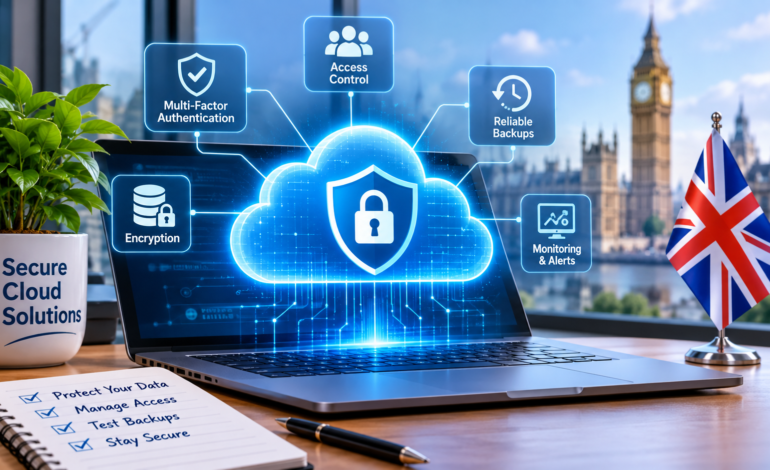
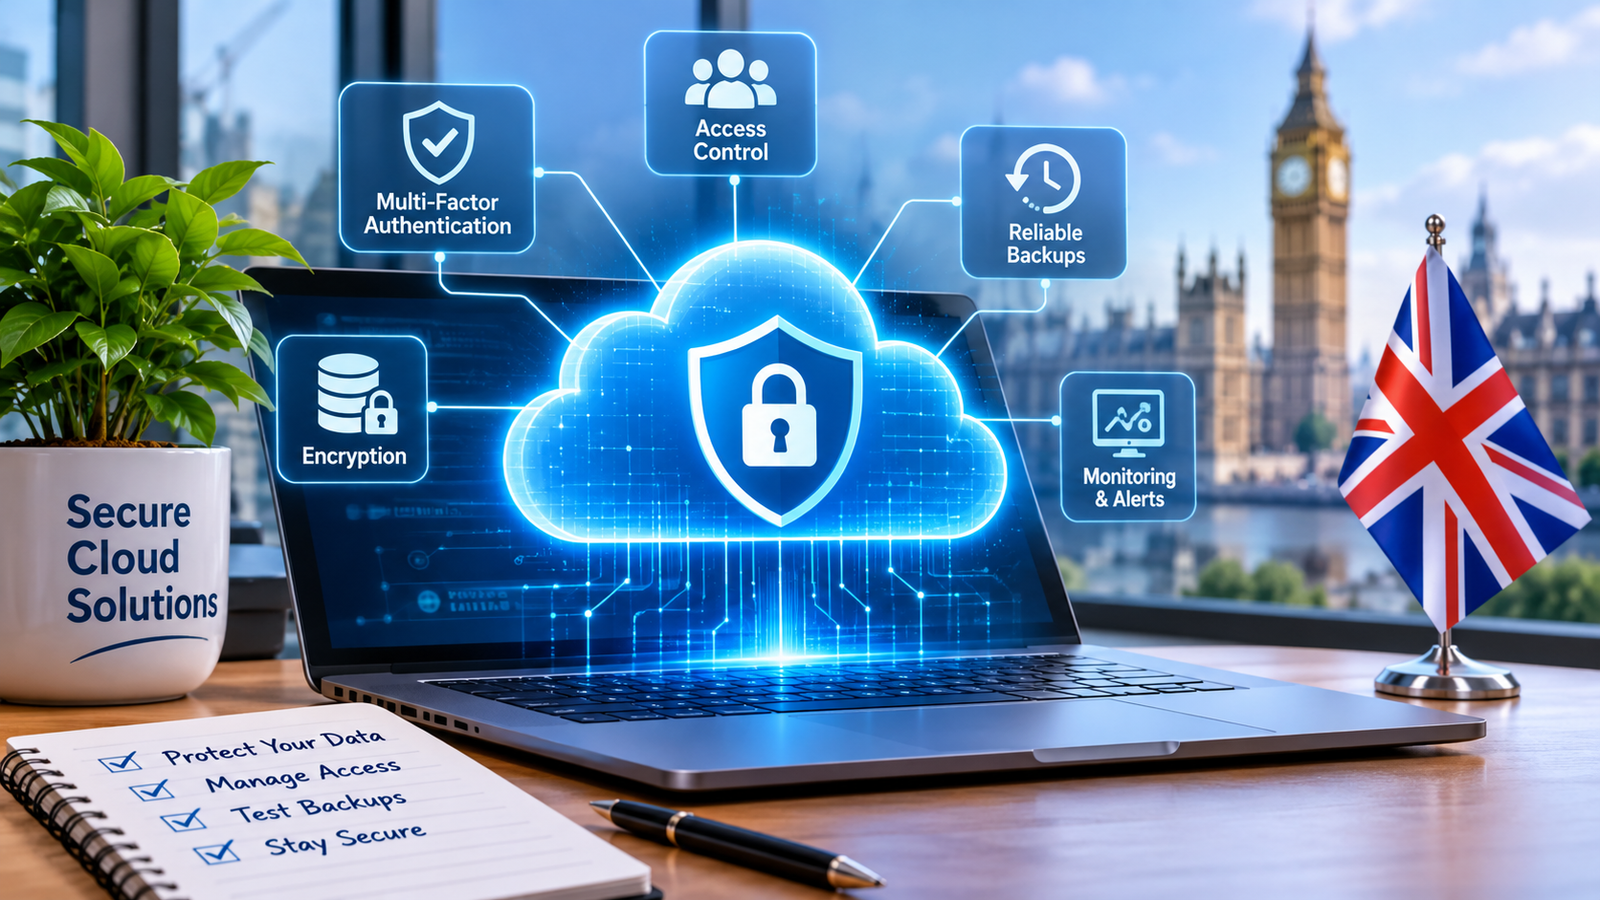
Quick answer: Secure cloud solutions are not one product you buy. They are a set of controls that protect your data, accounts, and apps in the cloud: strong sign-in, limited access, encryption, tested backups, monitoring, and clear ownership. Your cloud provider secures the building. You secure everything you put inside it.
What are secure cloud solutions?
Think of renting an office in a managed building. The landlord looks after the walls, the power and the front door. You still decide who gets a key, what goes in the filing cabinets and whether the windows are locked.
Secure cloud solutions are everything you do on your side of that line. The UK’s National Cyber Security Centre (NCSC) publishes free guidance on choosing, configuring and using cloud services safely. It is a good place to check your own plan against.
Why this matters more in 2026
The numbers have moved, and not in a comforting direction.
- IBM’s 2026 Cost of a Data Breach Report puts the average breach involving public cloud data at $5.38 million.
- Breaches took an average of 247 days to find and contain. That was the first rise in five years.
- UK organisations averaged £3.13 million per breach.
Here is the part most guides skip. AI tools are now in the mix. IBM found that AI-related incidents were rarely caused by the AI model itself. They usually came from weak cloud set-up around it: exposed APIs, loose plug-ins and misconfigured settings.
The good news: firms that used security automation heavily saved about $1.93 million per breach on average.
The 6 controls that do most of the work
You do not need a huge budget to begin. Start with these six.
- Strong sign-in. Turn on multi-factor authentication (MFA) for everyone. Use an authenticator app or a security key. Text-message codes are better than nothing, but they can be hijacked.
- Least-privilege access. Give people only the access their job needs. Nothing more. If someone moves team, change their access that week.
- Encryption. Data should be scrambled when stored and when sent. Most major providers offer this. Check that it is switched on.
- Tested backups. File syncing is not backup. If a file is corrupted or locked by ransomware, sync copies the damage. A real backup is separate, versioned and tested.
- Monitoring. Turn on logs and alerts. Then name one person who sees them. An alert nobody reads is just noise.
- Setting checks. Most cloud incidents come from simple slips: a public storage folder, an open port, an old admin account. Run a regular check for these.
Who owns what? (The shared responsibility model)
This is where many businesses get caught out. They assume the provider handles everything.
| Area | Your provider | You |
| Physical data centres | ✅ | |
| Hardware and core network | ✅ | |
| User accounts and passwords | ✅ | |
| Who can access what | ✅ | |
| Your data and how it is shared | ✅ | |
| Settings and configuration | ✅ | |
| Staff training | ✅ |
If a storage folder is left public, that is on you, not them.
Secure cloud solutions vs secure cloud storage
These get mixed up often. Cloud storage is one piece: where your files live. Secure cloud solutions cover the whole picture: sign-in, access, apps, backups and monitoring. This guide is about the bigger picture. It does not rank storage brands.
Your 30-day plan
Week 1: Map it. List every cloud tool your team uses. Note who the admins are and where sensitive data sits. Most teams find tools they forgot about.
Week 2: Lock the doors. Switch on MFA for all users. Give admins a separate account for admin work only.
Week 3: Clean up. Remove accounts for people who have left. Check sharing settings for anything set to “anyone with the link”. Close what you do not need.
Week 4: Prove it works. Restore a real file from backup and time it. Set up alerts for odd sign-ins. Write down who responds, and how.
That is a solid baseline in a month.
5 questions to ask any provider or partner
Before you sign anything, ask:
- Which security tasks are mine and which are yours? Can I have that in writing?
- Where is my data stored? Can I choose a UK or EU region?
- Who holds the encryption keys?
- What happens in the first hour of a security incident? Who calls me?
- Can you show me a recent restore test and your certifications, such as ISO 27001 or Cyber Essentials?
A good provider answers plainly. Vague replies are a warning sign.
Three mistakes to avoid
- Buying tools nobody runs. A smaller set of well-managed controls beats a big stack of ignored dashboards.
- Never testing recovery. You do not know your recovery time until you try it.
- Forgetting AI tools. If staff paste company data into unapproved AI apps, that data is outside your control. Set a simple rule on which tools are allowed.
FAQs
What are examples of secure cloud solutions?
Examples include MFA and identity tools, encrypted storage, isolated backups, cloud settings checkers and monitoring services. The right mix depends on what you run and what data you hold.
Is the cloud safe for business data?
It can be, but safety depends mostly on how you set it up. Providers secure the infrastructure. You secure accounts, access and settings.
Where should a small team start?
Start with MFA, then backups, then access clean-up. These three cut a lot of everyday risk and need little more than time.
Final thought
Secure cloud solutions are not about buying more tools. They are about knowing what you own, locking the basics and testing that your plan works. Most breaches start with small, fixable gaps.
Pick one step from the 30-day plan and do it this week. MFA is a great first choice.